KubeRange
A Kubernetes attack range with 83+ scenarios mapped to MITRE ATT&CK
What it is
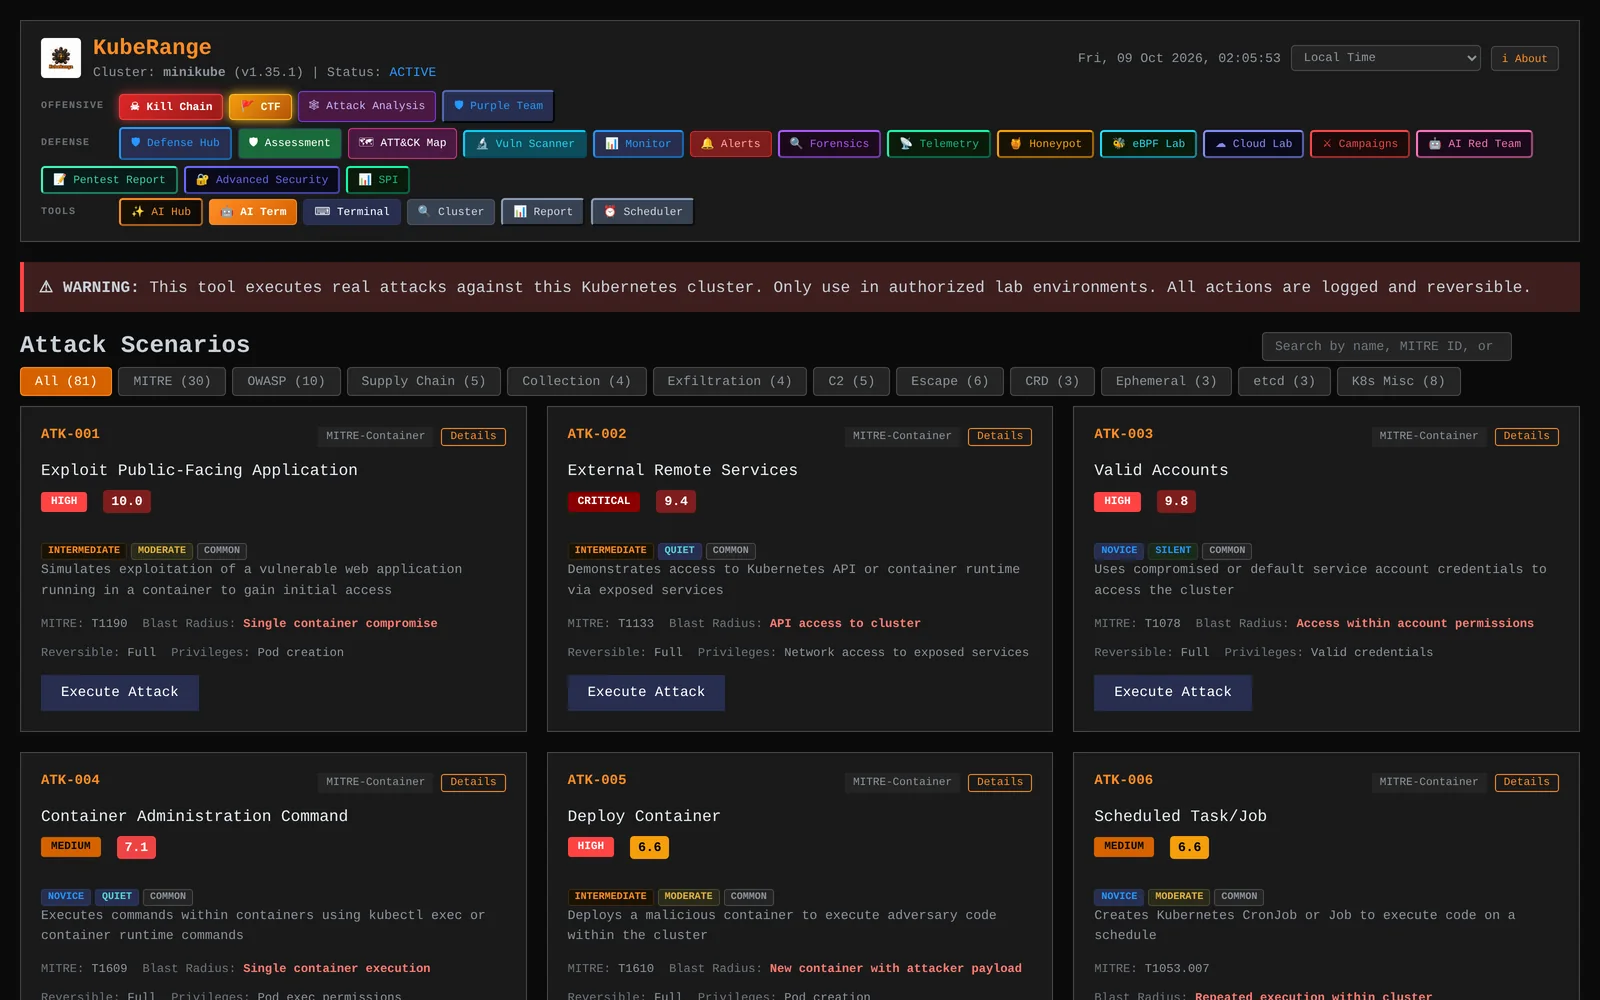
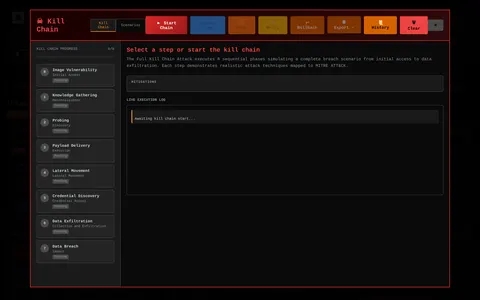
KubeRange is a Kubernetes security lab I built for isolated training environments. It runs as a privileged pod inside a throwaway cluster and lets you execute realistic attack techniques, then study and roll back exactly what happened. It is strictly for authorized labs, CTFs, and defensive research, never production.
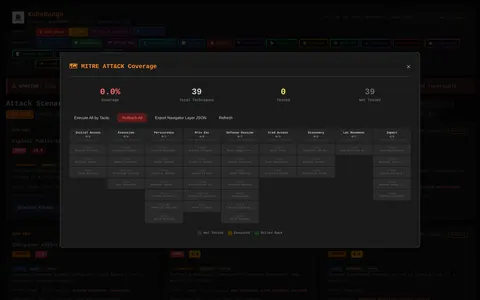
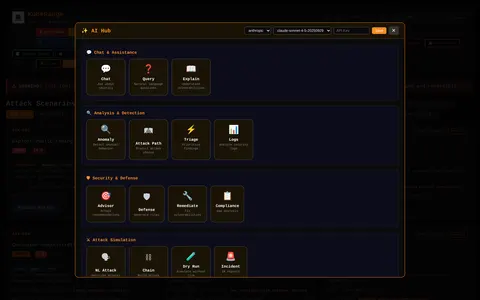
The whole thing is a single Go binary using client-go to talk to the cluster, with net/http and WebSocket serving a single-page dashboard that includes a live PTY terminal. The design principle is full reversibility: every created, modified, or host-level change is recorded in SQLite so rollback is idempotent and safe to repeat. The attack catalog is organized against the MITRE ATT&CK container matrix and the OWASP Kubernetes Top 10.
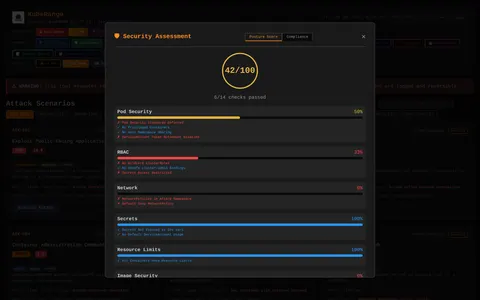
Alongside the offensive catalog it carries defensive tooling, which is the part I care about most: zero-trust network-policy synthesis, RBAC remediation, a Trivy-backed scanner, a runtime monitor, and compliance scoring against CIS and NSA/CISA benchmarks.
Features
- 83+ attack scenarios across MITRE ATT&CK and the OWASP Kubernetes Top 10
- Full reversibility, with every change tracked in SQLite for one-click rollback
- Defensive features: network-policy synthesis, RBAC remediation, chaos tests
- Vulnerability scanning and a runtime monitor for processes, files and flows
- Single-page dashboard with a PTY terminal and an ATT&CK heatmap
- Hardening built in: CSP, rate limiting, timing-safe auth, encrypted keys
Stack
83+ attack scenarios · ~148,000 lines of Go · 60+ internal packages